


A suspected negative SEO attack needs evidence, not panic. This guide provides a practical incident-response workflow for traffic drops, hacked content, spam links, scraping, fake removals and other threats.
A negative SEO attack is an attempt to damage another website’s search visibility or reputation through interference such as hacked content, malicious redirects, deceptive removal requests, or manipulative links. A sudden traffic drop is a reason to investigate, not proof that a competitor attacked you. Technical failures, tracking changes, shifting demand, and stronger competing pages can produce similar symptoms.
If you suspect negative SEO, preserve evidence, check for an active security problem, identify which pages and signals changed, and fix the mechanism you can verify. Do not start with a mass disavow, delete useful pages, or buy traffic to make the numbers look healthier. This guide explains how to move from suspicion to a documented response without turning an ordinary SEO problem into a larger incident.
First, Confirm That There Is a Real Incident
Write down the earliest confirmed change, not simply the day someone noticed it. Record the reporting time zone, affected URLs, countries, devices, queries, and acquisition channels. Compare complete periods with comparable weekdays. A partial day or a different report filter can make a normal pattern look like an emergency.
Keep three statements separate: what happened, what might explain it, and who caused it. An unauthorized redirect is an observable problem. A malicious actor is one possible explanation. Naming a particular competitor requires different evidence. You can contain a confirmed problem without proving who initiated it.
Check Google Search Console
Open the property that covers the affected URLs and check these reports before changing the site. Save dated exports or screenshots so later edits do not erase your baseline.
- Manual actions: check the issue, affected scope, and associated messages. An empty report does not explain every ranking decline.
- Security issues: look for hacked content, malicious downloads, or deceptive pages. Treat a confirmed warning as a security priority.
- URL Inspection: compare the indexed information with the live page’s accessibility, content, canonical signals, and indexing directives.
- Performance: compare affected pages and queries rather than relying only on the sitewide chart.
- Links: investigate unusual patterns, remembering that the Links report is a sample, not a complete backlink inventory.
A manual action follows human review; an algorithmic change is not listed as a manual action. Follow Google’s Manual actions guidance when that report identifies a problem. Use the separate Security issues process for a reported compromise; the two reports are not interchangeable.
Build an Evidence File Before Editing
For each finding, store the source URL or report, timestamp, observed behavior, affected scope, owner, and next check. Keep screenshots alongside original exports and relevant logs. Record missing evidence too: “no manual action reported” is useful context, but it is not a clean bill of health for the entire website.
Restrict access to this file. Server logs and support messages can contain personal information or security details. Share the minimum necessary with your host, developer, or incident specialist instead of posting unredacted material publicly.
Give each hypothesis a check that could disprove it. If you suspect injected content, identify where it appears and which clean version it differs from. If you suspect lost crawling access, look for failed requests and the responsible rule. “Our traffic is down” describes an outcome, not a mechanism, and cannot tell the developer what to repair.
Prioritize impact before certainty about motive. Visitors exposed to malicious redirects need protection now. An unfamiliar backlink with no associated harm can wait for review. Record that distinction so a dramatic alert does not divert the entire team from a less conspicuous but confirmed outage.
Rule Out Common Non-Attack Causes
Start with your own change history: releases, plugins, themes, DNS, redirects, CDN rules, consent settings, and analytics tags. Test representative affected pages and unaffected controls. Check that the intended page is accessible and still contains the expected content. A successful homepage check says little about a broken product template.
Use the following triage table to choose the next investigation. It is a decision aid, not a way to diagnose an attacker from one metric.
| Observed symptom | Check next | Avoid assuming |
|---|---|---|
| Analytics sessions fall; Search Console clicks remain steady | Tags, consent, filters, and landing-page tracking | Google rankings collapsed |
| One template loses visibility after a release | Rendering, status codes, canonical and indexing changes | The whole domain was penalized |
| Clicks decline while impressions remain similar | Query mix, CTR, position, and result appearance | Spam links caused the decline |
| Unexpected pages or redirects appear | Security findings, access history, files, and configuration | Removing one visible example fixes everything |
| Unfamiliar backlinks appear without other changes | Representative links, their context, and any manual action | Every unfamiliar domain needs disavowing |
Search Console clicks and GA4 sessions measure different things and should not be expected to match exactly. Use their direction and scope to form a question, then inspect the relevant system. If only one country or device changed, preserve that segment instead of averaging it away.
Also consider demand, seasonality, competing results, and search-system changes. Google’s guide to debugging search traffic drops covers these alternative explanations. A coinciding search update or backlink alert is context, not proof of causation.
Respond by Attack Type
Choose the narrowest response supported by the evidence. Several problems can coexist: a genuine security incident does not prove that every recent backlink is harmful. Give each confirmed mechanism its own owner and validation step.
Hacked Pages, Redirects, or Injected Content
If visitors are exposed to malicious behavior, prioritize containment with your host or security specialist. Preserve relevant logs and a restricted forensic copy where practical. Do not delay protecting visitors just to collect a perfect record, and do not casually download or open suspicious files.
Investigate unauthorized users, vulnerable software, altered templates, injected database content, and configuration changes. Restore verified clean material, close the entry point, revoke unauthorized access, and replace compromised credentials through a secure process. Restoring a backup without addressing the vulnerability can leave the same route open.
Agree on a safe change window and rollback plan with the technical owner. Preserve the known-good configuration separately from the suspected compromise. After cleanup, watch for the same unauthorized change returning; recurrence means the investigation is not finished. The search team can document affected URLs, but should not treat editing page text as a substitute for investigating server access.
Validate more than the first example URL. Check affected templates, redirects, linked resources, and relevant device or referral conditions with appropriate security tooling. A page that looks normal to an administrator may behave differently for another visitor. Escalate customer-data exposure or payment-page compromise to qualified security and privacy specialists.
Google’s Security issues guidance explains its findings and review process. Address all reported issues across the site, test the fixes, and then use the report’s review option where applicable. A search review does not replace technical cleanup.
Spam or Manipulative Backlinks
A new-link alert records a tool’s discovery, not necessarily the date a link was created. Examine representative source pages, anchor text, destinations, and patterns. A third-party “toxicity” label is not a Google manual action. Include the site’s own previous link-building activity in the investigation rather than assuming every suspicious link was placed by an outsider.
Google says most sites do not need disavow. Consider it only when a substantial pattern of artificial, spammy, or low-quality links has caused, or is likely to cause, a manual action. If that threshold is met, document removal efforts where practical and follow Google’s Disavow instructions. Keep a copy of any existing file: a replacement upload supersedes it.
Do not respond to a threat by buying link removal from an unverified sender. Preserve the message and involve the appropriate specialist. Bulk disavowing legitimate domains can create a new problem while leaving the original technical or content issue unresolved.
If outreach is appropriate, use independently verified contact details and keep a record of the request and response. Avoid opening suspicious downloads offered as “proof.” Your evidence should explain which links are problematic and why; an export of every low-scoring domain is not a defensible substitute for reviewing the pattern.
Scraped or Duplicated Content
Record the copied URLs, relevant passages, discovery dates, and your publication or revision evidence. Determine whether the material is a short attributed quotation, authorized syndication, or substantial unauthorized copying. Those situations call for different responses; duplication alone does not prove sabotage.
Check your own canonical signals, internal links, authorship information, and publication workflow. These make the original easier to understand but do not control another publisher’s pages. Preserve original research, images, and supporting records that demonstrate your contribution.
For suspected infringement, use the host or platform’s documented process and obtain legal advice when needed. Do not file speculative claims or assume a complaint guarantees removal or ranking recovery. If copying is widespread, prioritize commercially important examples instead of abandoning useful content to chase every scraper.
Fake Removals, Reports, or Reputation Attacks
Verify alarming emails through the platform’s official dashboard or a known contact route, not the message’s login link. Preserve headers, account notices, affected URLs, and correspondence. Distinguish an actual platform decision from someone merely claiming that they reported your website.
For a disputed removal, identify the stated reason and follow the applicable appeal process with factual evidence. For an impersonation or review problem, preserve the profile and publication details before reporting it. Do not publish accusations you cannot support or respond by making false reports yourself.
Keep reputational harm and search-performance changes separate in your incident record. A hostile post may require a communication response without explaining a ranking decline. Assign responsibility for customer replies so security work does not become an uncontrolled public argument.
Bot Traffic and Resource Exhaustion
Compare origin and CDN logs with analytics. A burst of requests to expensive endpoints, rising error rates, or repeated resource-intensive operations may indicate abuse. A spike of analytics sessions alone does not establish server overload, and an IP address alone does not identify a person or organization.
Apply targeted controls with your infrastructure provider: rate limits, caching, capacity protection, or rules focused on confirmed abusive behavior. Check the effect on ordinary visitors, checkout, accessibility, and legitimate crawlers. Broad country blocks or aggressive challenges can cause collateral damage.
A Googlebot user-agent string can be impersonated. Use Google’s crawler-verification methods, such as matching published IP ranges or reverse DNS followed by forward verification, before making crawler-specific decisions. Keep the rule change and its rollback conditions in your incident log.
Separate suspicious activity from acquisition analysis rather than buying replacement visits to dilute it. Monitor request success, latency, errors, and completed customer actions after containment. Better-looking session averages do not demonstrate that the underlying abuse has stopped.
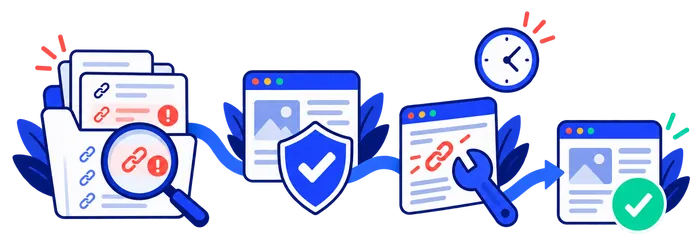
72-Hour Negative SEO Response Plan
Use this as an organizational sequence, not a recovery deadline. A small tracking fault and a compromised server require different resources. Active harm should be contained immediately; search reprocessing may take much longer.
- First four hours: assign an incident owner, preserve evidence, check security and manual-action reports, and involve hosting or security support when compromise is suspected.
- Day one: establish the affected scope and timeline. Compare changes in reports with releases, access records, logs, and representative URLs. List competing explanations.
- Day two: fix the verified mechanism, record the exact change, and test affected pages alongside unaffected controls. Avoid unrelated redesigns or link changes.
- Day three: document remaining risks, assign follow-up checks, and prepare any relevant review with evidence of completed remediation. Communicate facts and uncertainty to stakeholders.
A Hypothetical Investigation: Links or a Firewall Rule?
Imagine an online retailer receives a spam-backlink alert on the same morning that organic clicks decline. The initial theory is a link attack. This is a hypothetical example, not an SEOVisitor case study or a claim of measured recovery.
The owner compares affected pages and finds the decline concentrated in a category template. There is no reported manual action. The release record shows a new CDN rule; request logs show that the rule challenged verified crawler requests to those category pages. The backlink alert is real, but it does not explain that access failure.
The team corrects the specific rule, tests the category pages, and confirms that legitimate crawling and customer access work. It preserves the link sample for monitoring rather than uploading a speculative disavow file. The follow-up record separates immediate access validation from later search performance, which has not yet been established.
The lesson is not that spam links never matter. It is that the chosen fix should explain an observable mechanism and have a testable outcome. A ranking rise after several unrelated changes would provide much weaker evidence.
For a handoff, summarize the case in five lines: observed impact, confirmed evidence, action taken, validation completed, and next owner. In this example, the outstanding task is to review later search data, not to announce recovered rankings. If new evidence contradicts the firewall explanation, retain the earlier record and revise the hypothesis. A useful incident report can acknowledge uncertainty without leaving the next person unsure what to do.
Keyword Rank Tracker
Monitor selected keywords alongside your incident timeline with SEOVisitor’s optional paid Keyword Rank Tracker. It measures positions; it does not detect attacks, repair security issues, or restore rankings.
Keep keyword, location, and device settings consistent when reviewing positions. Use those observations alongside Search Console and business results, not as a substitute for server logs or security findings.
How to Prevent Future Attacks
Prepare a small response playbook before an emergency. List the people responsible for hosting, development, search reporting, customer communication, and escalation. Store recovery instructions where the team can access them if the website or a primary account becomes unavailable.
Use least-privilege access, multi-factor authentication, timely updates, tested backups, retained logs, and appropriate monitoring. Review unused accounts and integrations. Test a restoration process periodically; the existence of a backup does not prove that it is clean or usable. Give security changes an owner and a way to verify their effect.
For SEO resilience, maintain crawlable internal links, coherent canonical signals, useful original content, and a documented release process. Record important changes to templates, redirects, tracking, and access rules. These practices cannot prevent every attack, but they make unexplained changes easier to investigate.
Set alert thresholds around your own normal patterns rather than arbitrary universal percentages. A new domain may see volatile daily impressions; a mature shop may have predictable weekly demand. Combine business impact with technical evidence so the team does not ignore genuine warnings or escalate every ordinary fluctuation.
Keep a lightweight inventory of critical page templates and the actions they support. For a shop, that might include a category page, a product, checkout, and customer support. For a publisher, include an article, navigation, and subscription form. Rechecking the same representative journeys makes the next incident review more useful than collecting random screenshots.
Validate Recovery and Close the Incident
Close the immediate incident against explicit criteria: unauthorized changes are removed, the entry point is addressed, affected pages behave correctly, and abusive activity is controlled. Record who verified each item and what remains uncertain. A clean-looking chart is not a replacement for these checks.
Track search visibility and useful customer actions separately afterward. Keep comparison periods and segments consistent, note reporting delays, and avoid promising a return to the previous ranking. Where a review is pending, wait for its decision rather than repeatedly resubmitting. A resolved technical issue, a successful review, and improved rankings are different milestones.
Schedule the next review around the evidence needed, not constant dashboard refreshing. The infrastructure owner can verify request behavior promptly; the SEO owner needs enough complete reporting periods to interpret search changes. If access is healthy but visibility remains weak, reopen the content, demand, and competition hypotheses rather than assuming the attack must still be active.
Once urgent work is complete, return ordinary improvements to the normal SEO backlog. Document the strongest supported explanation, the changes made, and the evidence still missing. A disciplined negative SEO response protects visitors first and makes the next decision clearer without inventing certainty about attackers or recovery.
Frequently Asked Questions
Quick answers to common questions about negative SEO attack
Possible signs include hacked pages, unusual redirects, security warnings, spam-link spikes, resource exhaustion, or suspicious removals. A ranking drop alone is not proof; verify tracking, technical changes, demand, and competition.
No. Google says most sites do not need the Disavow tool. Use it cautiously only for a considerable pattern of manipulative links that caused or is likely to cause a manual action.
Check the Manual actions report in Google Search Console. Algorithmic ranking changes are not listed there, so also review technical health, content, search demand, and competitors.
Scraping can create confusion or reputation issues, but duplication does not automatically remove the original. Preserve evidence, strengthen canonical and internal-link signals, and use legitimate copyright or platform processes when appropriate.
There is no fixed timeline. Security fixes can be validated quickly, but crawling, reprocessing, reviews, and ranking recovery may take longer. Monitor verified signals instead of expecting an immediate return.
Save affected URLs, timestamps, report exports, screenshots, relevant logs, and the site's change history. Keep observations separate from suspected causes, and restrict access to records containing customer or security information.
Escalate promptly when you find unauthorized access, injected content, malicious redirects, customer-data exposure, or resource abuse. An SEO report can identify affected pages, but containment and closing the entry point require the appropriate technical owner.
Confirm that the verified problem is removed, its entry point is addressed, and affected pages and customer journeys work correctly. Monitor recurrence and keep later search-performance reviews separate from immediate technical validation.

Comments
Leave a Comment