


DNS does not improve rankings by itself, but availability, response reliability, HTTPS, caching and configuration errors can affect crawling and user experience. This technical guide explains what Cloudflare changes and how to test it.
DNS and Cloudflare affect the conditions that let visitors and search crawlers reach your website. Reliable name resolution, secure connections, suitable caching, and correct access rules can support a usable, crawlable site. They do not create relevance, guarantee indexing, or provide a ranking boost simply because you choose a particular provider.
The practical approach is to identify which layer changed and test its behavior. A DNS lookup failure, an origin certificate problem, a cached response, and a firewall challenge need different fixes. This guide explains those differences, preserves a safe migration process, and shows how to investigate a hypothetical Cloudflare problem without confusing a technical correction with proven SEO growth.
Does DNS Affect SEO?
DNS translates a hostname into the information needed to reach its service. If resolution fails, the request may never reach the web application. A healthy website behind an incorrect DNS record can therefore remain inaccessible even when the hosting dashboard says the server is running.
Google’s guidance on DNS and network errors explains that these failures prevent content retrieval and can reduce crawling. Treat persistent access failures as operational problems, not as evidence of a mysterious Cloudflare penalty. Improving availability is valuable without promising a particular ranking outcome.
Separate lookup time from the rest of delivery. A faster DNS answer cannot repair a slow database, an oversized image, or a broken application. Likewise, a quick cached response does not prove every visitor can successfully use a form or checkout. Measure the component related to the symptom.
A failure before HTTP may leave no matching entry in the application’s access log. That absence does not prove the visitor never tried to connect. Correlate the time with DNS and network evidence, then involve the host if necessary. Editing the page title or submitting a new sitemap does not correct a hostname that cannot be reached.
| Layer | Question to answer | Useful evidence |
|---|---|---|
| DNS | Does the hostname resolve as intended? | Record answers, delegation, resolver errors |
| TLS | Can both connection stages negotiate securely? | Certificate, hostname, connection errors |
| Edge and origin HTTP | Which system returned the response? | Status, redirects, cache and access logs |
| Delivered page | Is the intended content usable and indexable? | HTML, directives, rendering, completed tasks |
Use the same URL and a recorded timestamp when moving between these checks. Otherwise, a support conversation can mix an old DNS failure, a new cached page, and a different visitor’s screenshot as if they described one request.
What Changes When Cloudflare Is Enabled?
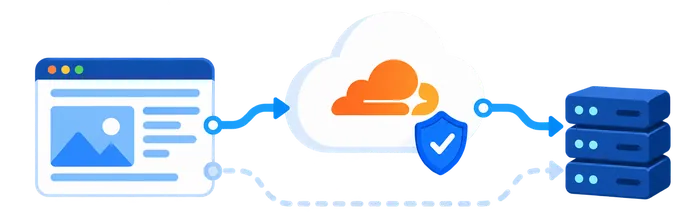
Cloudflare can provide authoritative DNS without proxying the website, or it can proxy compatible web records. With a proxied record, public resolution returns Cloudflare addresses and HTTP traffic passes through its network before reaching the origin. With DNS-only delivery, Cloudflare does not sit in that HTTP request path.
The proxy-status documentation distinguishes these modes. A, AAAA, and CNAME records can be proxy candidates; MX and TXT records are DNS-only. A verification CNAME may also need to remain unproxied. Check the service’s requirements rather than applying one setting to every record.
Document the hostname you are investigating. The main site, an asset subdomain, and a shop can follow different paths. “Cloudflare is enabled” is not enough information to explain which cache, certificate, or security rules apply to a particular request.
Also distinguish the authoritative DNS service for your domain from the recursive resolver a visitor uses. Changing a resolver on your own computer is not the same operation as changing the domain’s nameservers or proxy status. Write down which change was actually made before connecting it to a public website symptom.
Performance and Caching
A CDN can serve suitable cached resources without fetching them from the origin on every request. This can reduce repeated origin work, but a cache miss still depends on the upstream service. Compare repeat requests and uncached behavior rather than judging the whole system from one fast load.
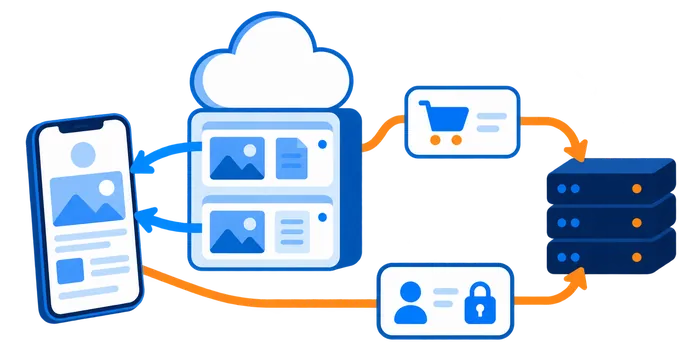
Cloudflare’s default cache behavior does not cache HTML or JSON by default, while robots.txt is cached by default. Rules, application integrations, and custom logic can change behavior. Inspect the actual configuration instead of assuming that enabling the proxy means every page is cached.
Personalized pages, account areas, carts, checkout, and previews need deliberate handling. Broad HTML caching without an application-aware design can deliver the wrong state or expose information. Check logged-out and authorized test-account journeys separately; never use another customer’s data as a test fixture.
Record what an optimization is intended to improve: asset delivery, response time, origin load, or a particular user task. Keep that outcome separate from rankings. Caching cannot compensate for irrelevant content, missing instructions, or a primary action that does not work.
Do not confuse DNS TTL with page-cache freshness. One concerns how long a DNS answer may be retained; another concerns a cached resource. Browser and application caches can add further layers. Changing a DNS record’s TTL does not purge an old article, and purging an article does not repair an incorrect DNS target.
HTTPS and Certificate Handling
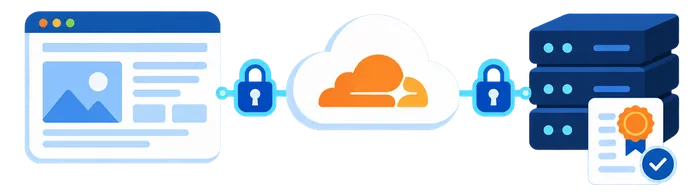
A proxied HTTPS site has two connection stages: visitor to Cloudflare, and Cloudflare to origin. A valid edge certificate does not establish that the origin certificate and connection are correct. Test both stages with the technical owner before enforcing a new redirect policy.
Full (strict) validates the origin certificate as well as encrypting the connection. Its requirements include an unexpired certificate, an appropriate trusted issuer, and matching hostname coverage. Correct the origin setup rather than weakening validation to hide a certificate error.
Flexible mode uses HTTP between Cloudflare and the origin. If that origin redirects HTTP to HTTPS, a loop can result. A lock icon on the visitor-facing connection does not make this equivalent to end-to-end HTTPS.
After the secure route works, check that internal links, assets, canonical signals, and sitemap URLs use the intended version. Mobile layout and content usability remain separate responsibilities; secure delivery does not automatically make a page usable on a small screen.
Plan rollback carefully if using Cloudflare Origin CA. Its certificate guidance warns of browser trust errors when traffic bypasses the proxy. An unplanned switch to DNS-only can therefore create another failure. Have the hosting specialist validate the alternate route rather than treating proxy removal as a universal troubleshooting step.
Make certificate maintenance part of the handoff. Record which hostnames are covered, who monitors expiration, and who can investigate renewal failures. A migration test confirms the current setup only; it does not guarantee that an unattended origin certificate will remain valid indefinitely. Keep private keys and account credentials out of shared SEO reports.
Cloudflare Problems That Can Hurt Crawlability
Investigate the response actually delivered, not merely whether a dashboard shows the zone as active. Save the URL, time, request conditions, status, response content, and relevant rule or log evidence. The same hostname can work for one visitor while failing for a different request pattern.
Blocking Verified Crawlers
Firewall, bot, rate-limit, and geographic rules can affect legitimate clients if their scope is too broad. Identify the rule responsible and the affected paths. Do not globally disable protection or allow every request with a familiar user-agent string just to make a test pass.
Follow Google’s crawler-verification guidance. Published IP ranges or reverse DNS followed by forward confirmation can help verify identity. A request claiming to be Googlebot is not sufficient evidence by itself.
Have the infrastructure owner apply a narrowly justified correction, then test the affected page and its required resources. Confirm the intended content is returned, not a challenge or generic error page. A successful browser visit under your own account does not establish that ordinary crawler requests receive the same result.
Keep the test conditions visible in the record. A logged-in editor, a monitoring service, a live inspection request, and an ordinary crawler request can encounter different rules. Use each result for the question it actually tests, and review continuing access rather than treating one successful request as permanent confirmation for every client.
Caching the Wrong Response
When the public page differs from the expected version, first verify what the origin should return. Compare the delivered content, status, canonical markup, and indexing directives. A successful HTTP response containing a login screen or outdated instructions is not equivalent to the intended article.
Correct the underlying rule or origin response before purging; otherwise the same wrong content can return. Cloudflare recommends targeted URL purging rather than routinely clearing everything. A full purge can increase origin demand as content is fetched again.
Re-fetch the affected URLs afterward and verify the result. An accepted purge request is not the same as a confirmed correct page. Include the relevant variants where custom cache keys distinguish them, and check whether an application or browser cache explains any remaining discrepancy.
For a content release, compare a recognizable element from the intended version, such as the updated instruction, alongside its status and directives. A cache-status label alone does not prove that the right article was delivered. Keep the verification specific enough that someone else can repeat it without relying on your browser session.
Redirect, Canonical, and Protocol Conflicts
List redirects at the application, server, plugin, and edge layers. Conflicting rules can bounce between protocols or hostnames. Choose the intended destination for each real URL variant, then inspect the full path instead of testing only the final page you reached manually.
Check the main hostname, its alternate version, HTTP entry points, and representative article paths. Legitimate permanent moves and intentional missing pages should retain their appropriate responses; do not turn every error into a homepage redirect. The final article should serve its intended content with consistent canonical and internal-link signals.
Google’s HTTP status documentation explains why status and content both matter. A 200 response does not guarantee indexing, while persistent access failures need attention. Do not change canonical tags merely because a page now passes through a different network layer.
Origin and DNS Mistakes
Review the intended A, AAAA, and CNAME targets, authoritative nameservers, and origin service. A stale IPv6 record, a missing hostname, or an origin firewall expecting an old connection path can cause inconsistent failures. Compare working and failing requests rather than repeatedly changing records without a hypothesis.
When moving providers, account for DNSSEC. An old parent DS record that no longer matches the signing setup can break validation. Cloudflare’s DNSSEC chain-of-trust guidance explains the dependency. Coordinate a supported migration with the DNS owner; do not copy keys or remove security settings casually.
Ask support to distinguish resolution, connection, certificate, and application failures. Include timestamps and the hostname rather than saying only “SEO dropped after Cloudflare.” A precise failure description makes the response safer and avoids unnecessary changes to content or indexing directives.
Safe Cloudflare Migration Checklist
Treat the move as a controlled infrastructure release. Assign an owner, preserve the known-good configuration, define acceptance checks, and agree on rollback conditions before the change window. If DNS and application hosting are both moving, test their dependencies separately where practical.
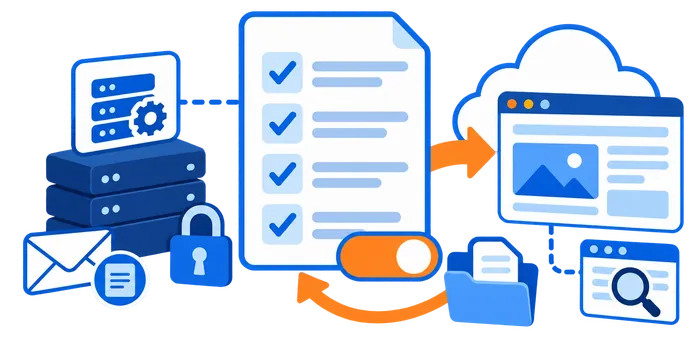
- Inventory records: compare web, mail, verification, CAA, SRV, and delegated subdomain requirements; do not rely only on an automatic scan.
- Document timing: review existing TTLs and resolver caching. Lowering a record TTL does not guarantee an instant nameserver transition.
- Verify the origin: confirm the correct site, hostname coverage, HTTPS support, and expected content before proxying.
- Plan DNSSEC: coordinate registrar records, signing keys, and the supported provider migration sequence.
- Choose proxy scope: proxy compatible web records deliberately and preserve required DNS-only services.
- Review delivery rules: document redirects, cache exclusions, security controls, and important response headers.
- Test real journeys: include articles, navigation, forms, login, and cart or checkout where applicable.
- Check SEO resources: inspect robots.txt, sitemaps, assets, canonical signals, and indexing directives.
- Monitor and retain evidence: track resolution failures, response errors, origin behavior, and the tested URL sample.
- Keep rollback viable: confirm the alternate route’s certificates and access requirements, not just the old nameservers.
For a signed zone, a coordinated approach can preserve DNSSEC during the move where provider support permits it. Cloudflare’s DNSSEC migration tutorial is an advanced procedure, not a checklist to improvise from memory. Escalate unfamiliar signing or delegation work to the responsible specialist.
A DNS-provider move is not automatically a change of website address. Keep domain-name, rebranding, and URL-migration decisions separate so the team does not introduce unrelated redirects or canonical changes during infrastructure troubleshooting.
Before closing the window, record which checks passed, who approved them, and what remains under observation. Keep the original configuration available until the new setup is stable. A successful homepage load is only one check, not proof that every subdomain, dynamic journey, and crawler path is healthy.
Define rollback by impact and evidence: an inaccessible primary journey or confirmed certificate failure needs a clear escalation path. Do not improvise repeated nameserver changes while caches are still producing mixed observations. The owner should know which component can be safely restored, which dependencies must be preserved, and how the restored route will be verified.
How to Test SEO After the Change
Use independent evidence across the request layers. Compare DNS answers from appropriate resolver locations, inspect redirects and headers, and load representative pages with their assets. Arrange origin-specific checks securely with the hosting team; do not expose a protected origin or bypass certificate warnings to complete a test.
In Search Console, compare the indexed information with a live inspection of important canonical URLs. A live success is a point-in-time access result, not a completed recrawl or an indexing guarantee. Continue reviewing genuine crawler requests and relevant logs after the release.
Build a small evidence bundle for failures: exact URL, timestamp and time zone, client conditions, response status, relevant headers, expected content, actual content, and the matching log or request identifier where available. Do not include secrets or customer data. This is more actionable for support than a screenshot of a traffic chart with no corresponding request evidence.
| Symptom | Investigate next | Verify the correction |
|---|---|---|
| Hostname fails to resolve | Records, delegation, DNSSEC validation | Consistent intended answers |
| HTTPS loops or certificate errors | Both TLS stages and redirect rules | Valid secure route without a loop |
| Public page is stale or incorrect | Origin response, cache rules, variants | Correct content and directives |
| Crawler gets a challenge | Verified request and matching security rule | Expected page and resources accessible |
A Hypothetical Investigation: An Article Behind a Challenge
Imagine a publisher activates proxying and a new security rule during the same release. The homepage works for the editor, but an article fails a crawler-oriented access check. This is a hypothetical scenario, not a measured SEOVisitor incident or a ranking-recovery claim.
The team records the article URL and timestamp, verifies the relevant request identity, and compares edge and origin evidence. The matched security rule returns a challenge before the intended article is delivered. Correct DNS answers therefore do not resolve this particular failure.
The owner narrows the problematic rule appropriately, retests the article and its resources, and checks ordinary visitor journeys. The immediate success criterion is restored access to the intended content. Any later search-performance change remains a separate observation; no numerical uplift or recovery deadline is invented.
Compare delivery performance under matching conditions afterward. Record location, device, page type, and cache state. A warm asset request and a first uncached page load are not equivalent tests. Review field user-experience data as well as repeatable diagnostics, while allowing for the reporting period and unrelated site releases.
Keyword Rank Tracker
Monitor selected keyword positions alongside your infrastructure change log with SEOVisitor’s optional paid Keyword Rank Tracker. It records ranking trends; it does not diagnose DNS faults, repair Cloudflare settings, or guarantee recovery.
Keep Search Console impressions and clicks, analytics outcomes, and request-level health separate in the review. Seasonality, competing results, content changes, and tracking changes can affect business reports. Establish that the technical mechanism works before attributing a ranking movement to it.
DNS and Cloudflare SEO: Final Verdict
Choose infrastructure for reliable resolution, secure delivery, appropriate caching, and manageable protection. DNS and Cloudflare are not substitutes for useful content or a coherent SEO strategy. Their practical SEO value is keeping the intended pages available and usable, not manufacturing search demand.
Close each investigation with the affected layer, confirmed cause, specific correction, validation evidence, and remaining uncertainty. A reproducible technical fix is a stronger result than a claim that changing providers automatically improved Google rankings.
Frequently Asked Questions
Quick answers to common questions about DNS and Cloudflare SEO
No. A DNS provider is not a direct ranking shortcut. Reliable resolution, uptime, secure delivery, and correct configuration can support crawlability and user experience, while outages and errors can cause problems.
No. A, AAAA, and CNAME records serving compatible web traffic are common proxy candidates. Email, domain-verification, and non-HTTP service records often need to remain DNS-only.
Caching can cause problems if it serves stale robots directives, error pages, personalized content, or the wrong canonical response. Use deliberate cache rules, exclusions, testing, and targeted purges.
Full (strict) is generally the appropriate secure choice when the origin has a valid certificate. Test the complete HTTPS and redirect path before enforcing it.
Use Search Console URL Inspection and a live test, review Cloudflare and origin logs, verify status codes and rendering, and confirm that firewall or bot rules do not challenge verified crawlers.
Compare the affected URL's response, Cloudflare events, and origin logs with your technical owner. Identify which layer returns the error or challenge before changing rules, and test representative pages after the specific fix.
Preserve the current DNS records, relevant proxy and cache rules, certificate configuration, redirects, and a timestamped baseline. Assign an owner and rollback plan, including checks for web pages, email records, and other services that use the domain.
No. A live test checks current accessibility, while indexed information reflects Google's recorded version. Review both and distinguish a working delivery fix from later crawling, indexing, and search-performance changes.

Comments
Leave a Comment